Attack surface management
See everything your company exposes to the internet, ranked by what attackers exploit.
- Passive checks hosted, full scans on your server
- Free check of your email, DNS and exposed names, graded A to F, first results in about 40 seconds
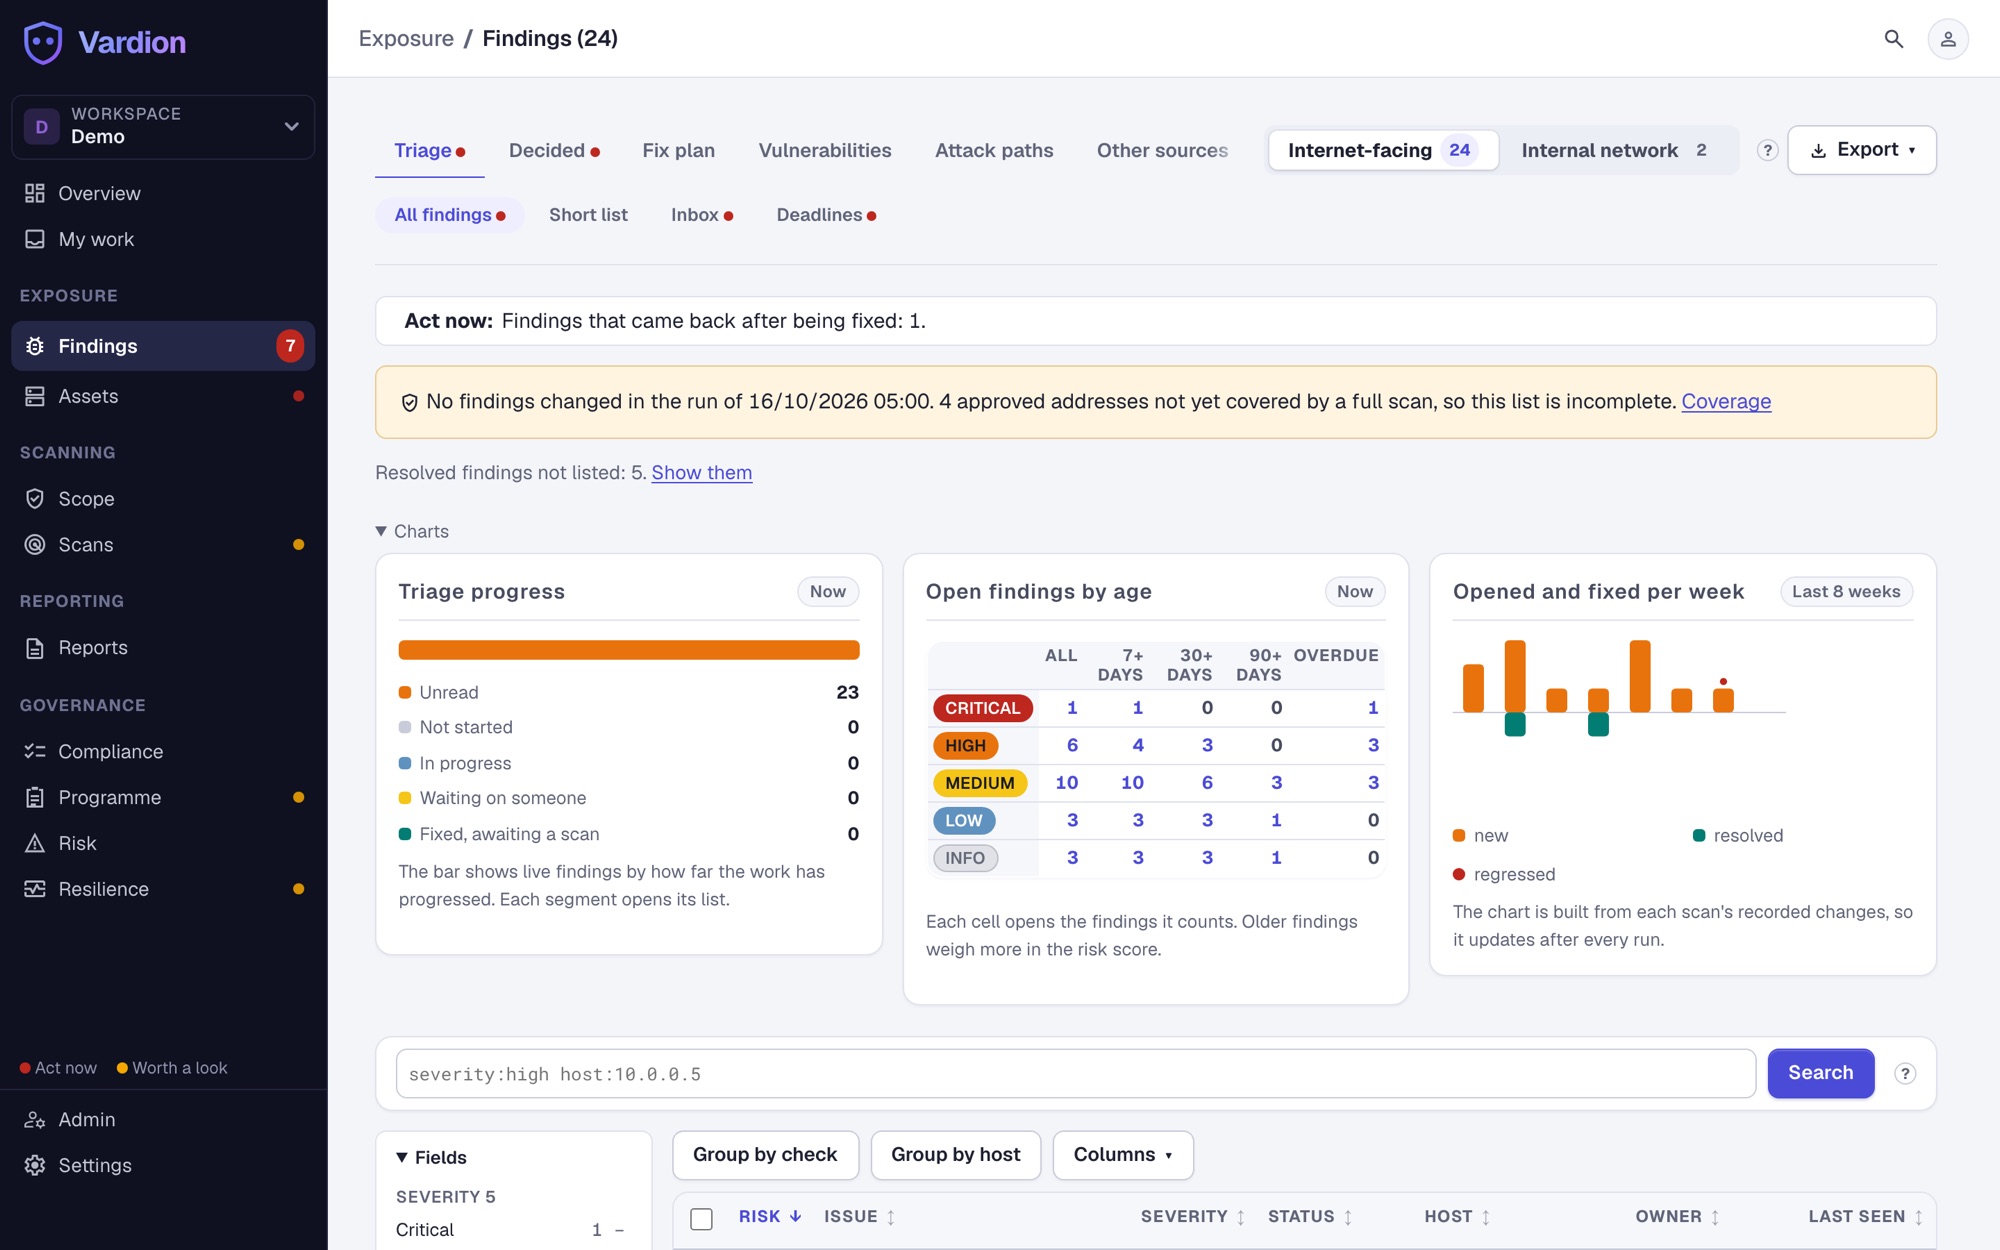
Risk-based prioritisation
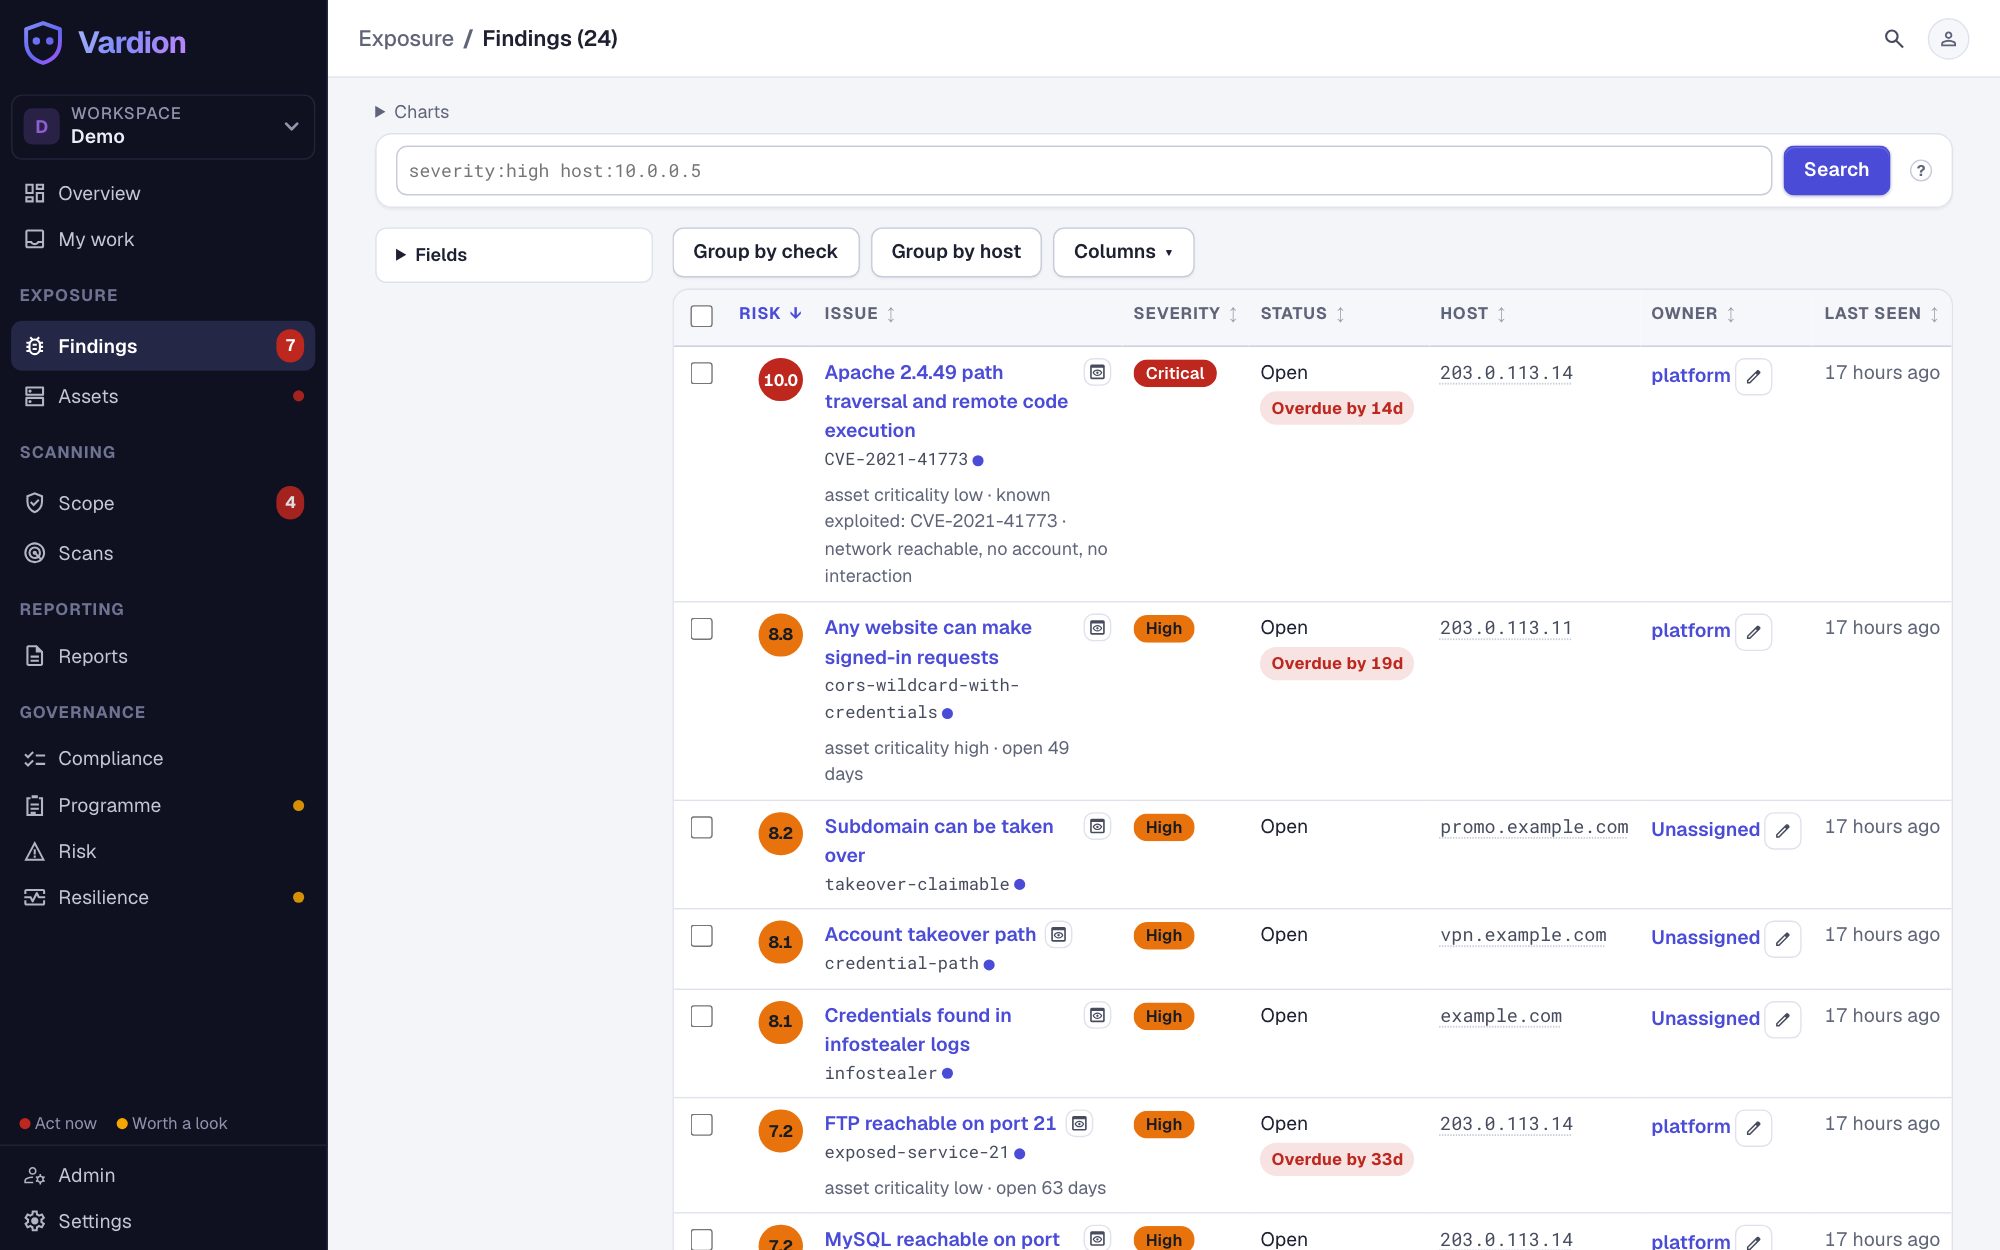
Each finding is scored 0 to 10 by exploitation and age, each system by how critical it is. Fix the riskiest first.
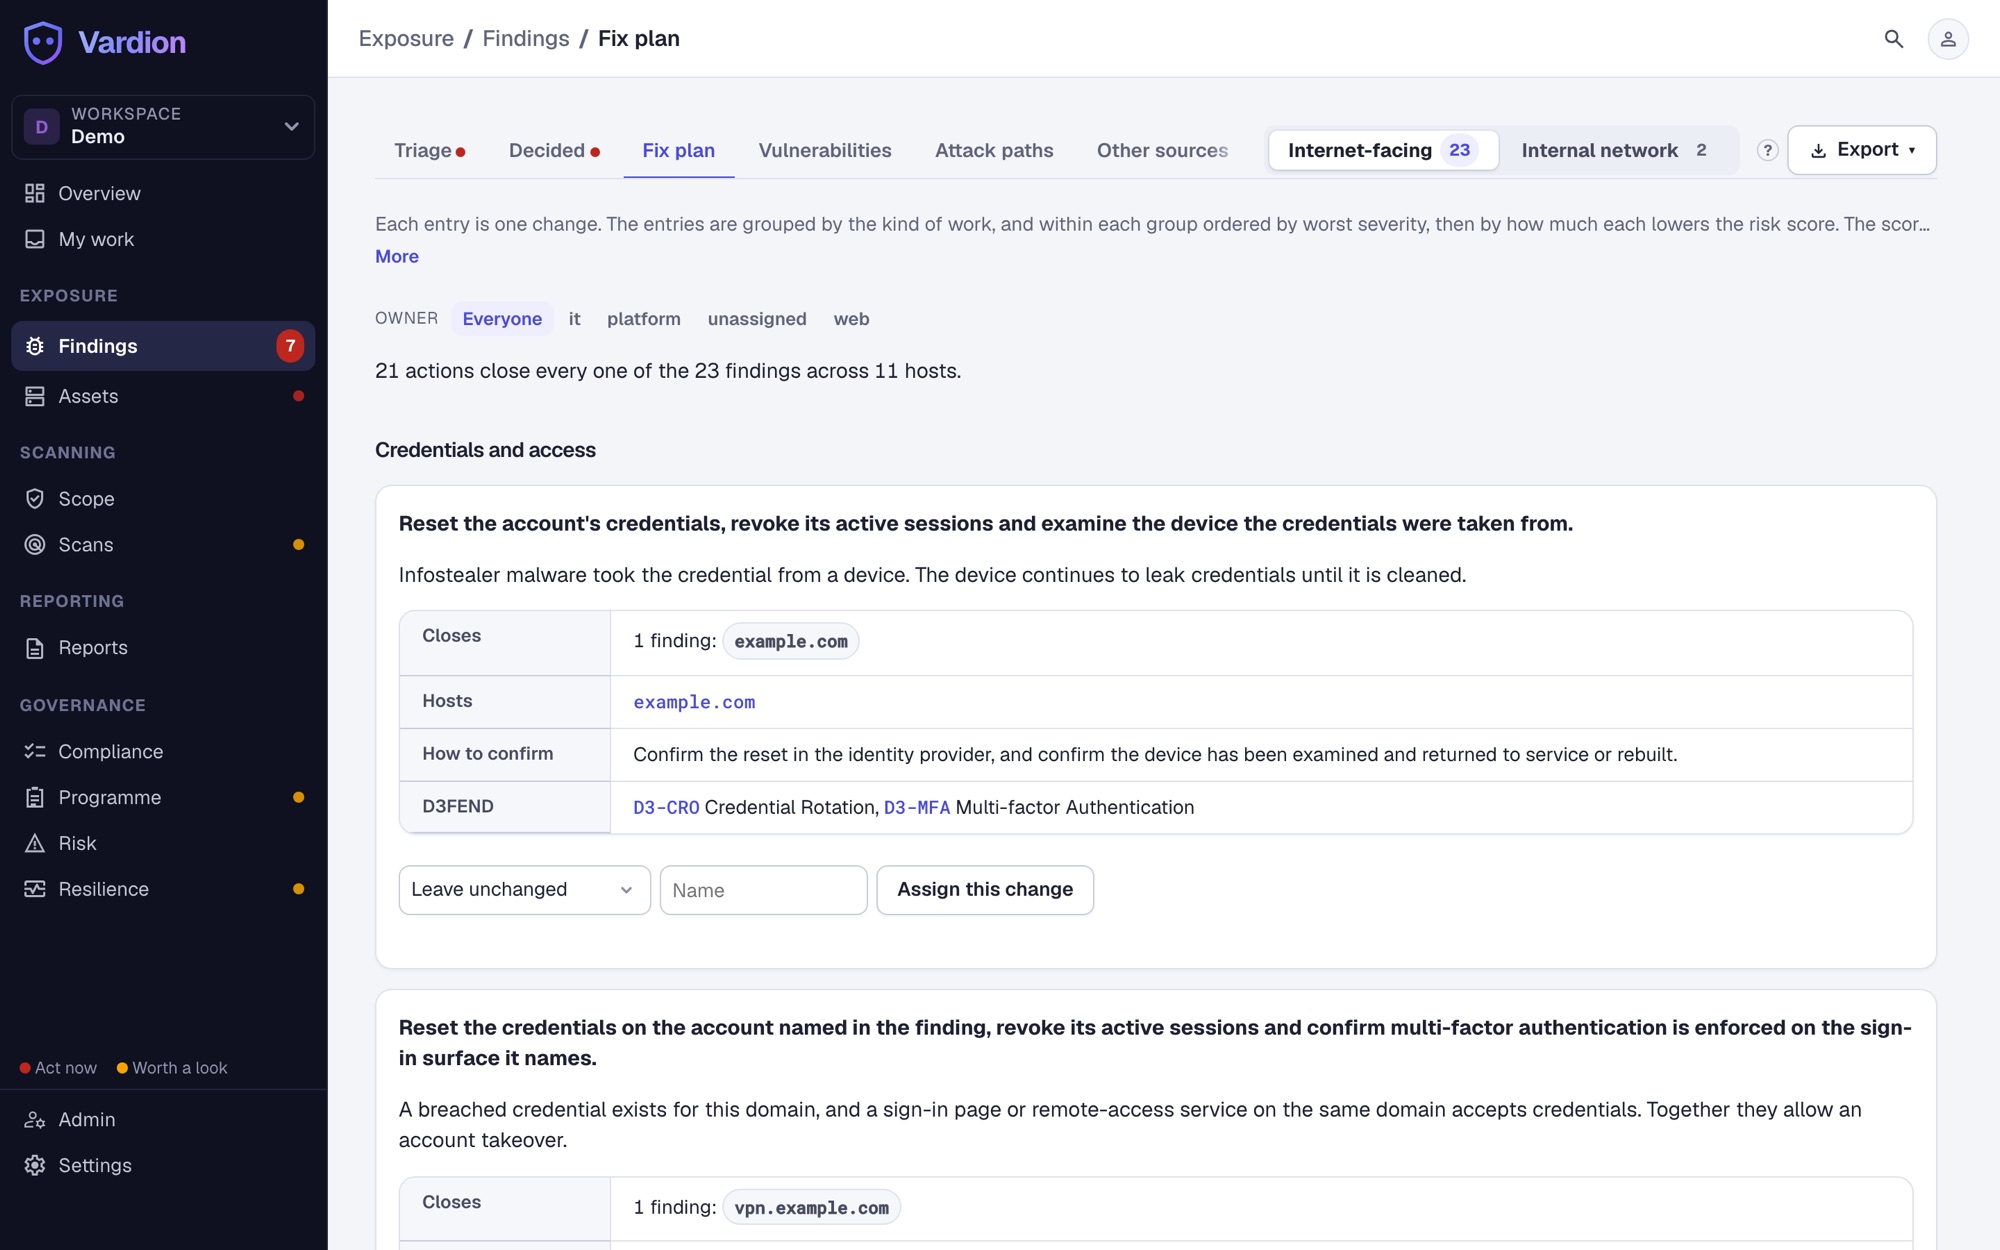
Remediation plans
In the fix plan, a firewall rule on 9 hosts is 1 task, not 9.
- Ready configuration lines for nginx and Apache
- A one-host retest that confirms the fix
New critical vulnerabilities
Vardion shows what needs updating and which websites, plugins, servers and code a critical flaw touches. Your IT provider or your tools install the updates.
How a scan becomes a fix plan
In the demo, 24 results become 22 changes.
Scanner output
[CVE-2021-41773] [critical] https://203.0.113.14/cgi-bin/.%2e/.%2e/.%2e/.%2e/etc/passwdChange 1 of 22
Apply the vendor's fix for CVE-2021-41773 (Apache 2.4.49 path traversal and remote code execution).
First: known exploited: CVE-2021-41773; network reachable, no account, no interaction.
Scanner output
[version-banner] [low] https://203.0.113.10:443
[version-banner] [low] https://203.0.113.11:443
Change 19 of 22
Remove the product version from the Server, X-Powered-By and X-AspNet-Version response headers.
What Vardion scans
Email and lookalike domains
SPF, DKIM, DMARC, MTA-STS and DNSSEC. Lookalike domains ranked by how ready each is to send mail.
Leaked staff passwords
Staff accounts found in breaches and infostealer logs.
Websites
Headers, cookies, TLS and exposed files on every site.
Cloud settings
AWS, Azure, Google Cloud, Microsoft 365 and Google Workspace. Checked daily, and drift opens a finding.
Your whole estate
Every subdomain, server, open service and certificate under your domains.
Fewer false positives
A site that answers every path is reported once, not as 16 exposed files.
- A web firewall a scan finds is noted on the host, never raised as a finding.
- A false positive marked once stays closed unless it returns worse.
Built on established open-source scanners, each version fixed and checked.
Safe for production
Only what you approve
Nothing is scanned until you approve the address, range or cloud account.
Gentle by default
At most 50 requests a second per host, and no denial-of-service or intrusive tests.
Industrial and medical ports: port scan only
S7, Modbus, DNP3 and DICOM are found and never probed further.
Every change recorded
A tamper-evident log of who changed the scope and when.
Frequently asked questions
We already run a vulnerability scanner. Why add Vardion?
Keep it. Tenable, Qualys and Defender connect by API and other scanners by file, into one ranked list.
How is this different from a penetration test?
A penetration test runs once or twice a year. Vardion checks in between and gives the tester a ready scope.
What exactly does a scan send?
TCP connections to the ports you choose, then web, TLS and vulnerability checks, with every web request carrying the User-Agent Vardion-ASM/1.0. The scan profile lists every setting.