Board reporting and cyber risk quantification
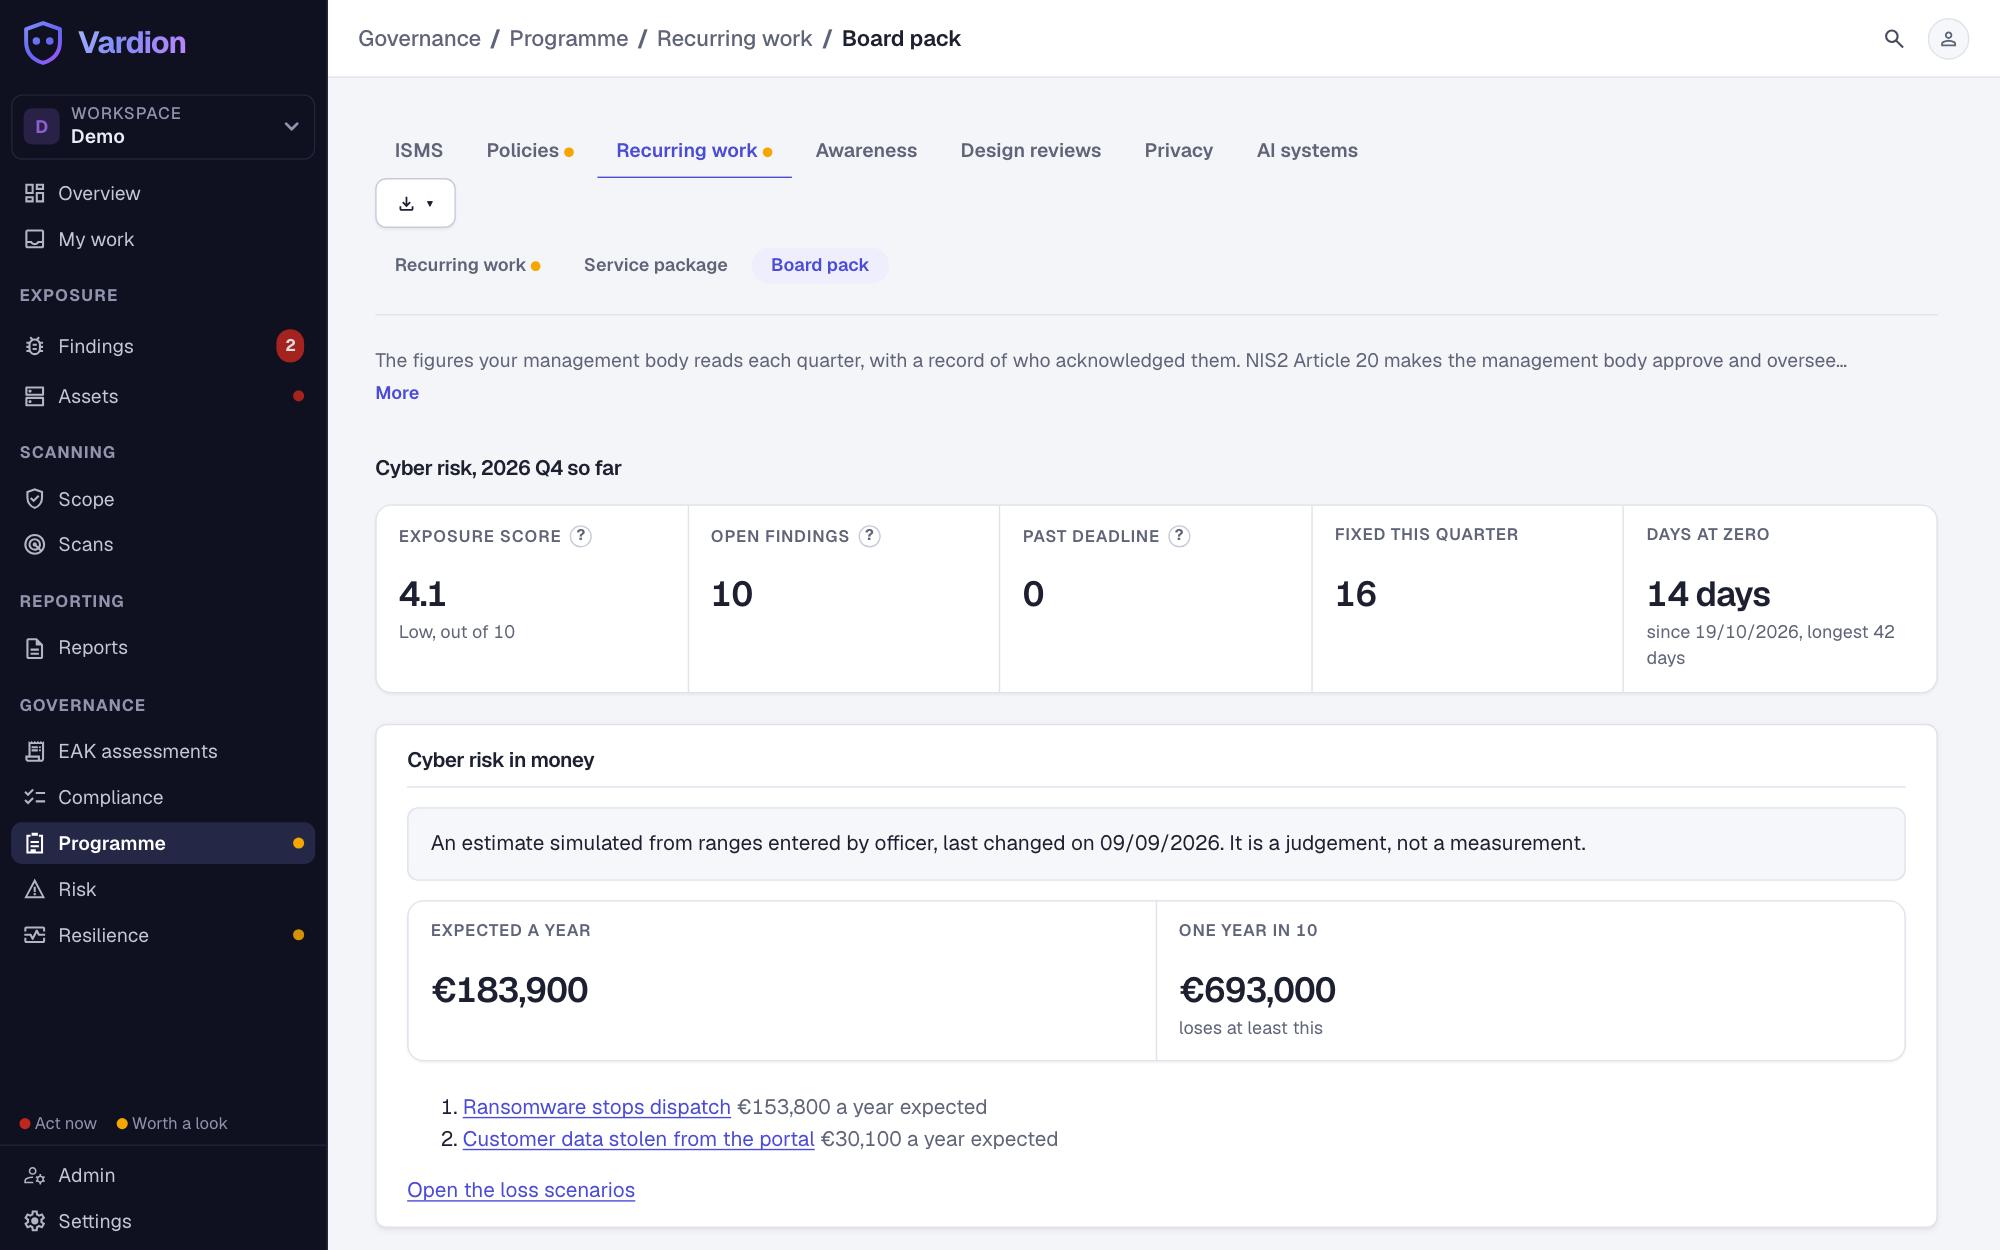
Under NIS2 your board approves the security measures and answers for them. Vardion gives it what it needs each quarter, from your own records.
- The board pack every quarter, from your own records
What NIS2 asks of management
Approve and oversee the measures
Record who approved each policy and when. Each director acknowledges the quarterly board pack from their own account. A breach can be fined up to €200,000 (Law 5160/2024, Article 26(9)(a)).
Follow training
Track management training as a recurring duty, with the date of each round. A breach can be fined up to €100,000 (Law 5160/2024, Article 26(9)(b)).
Drill down to the evidence
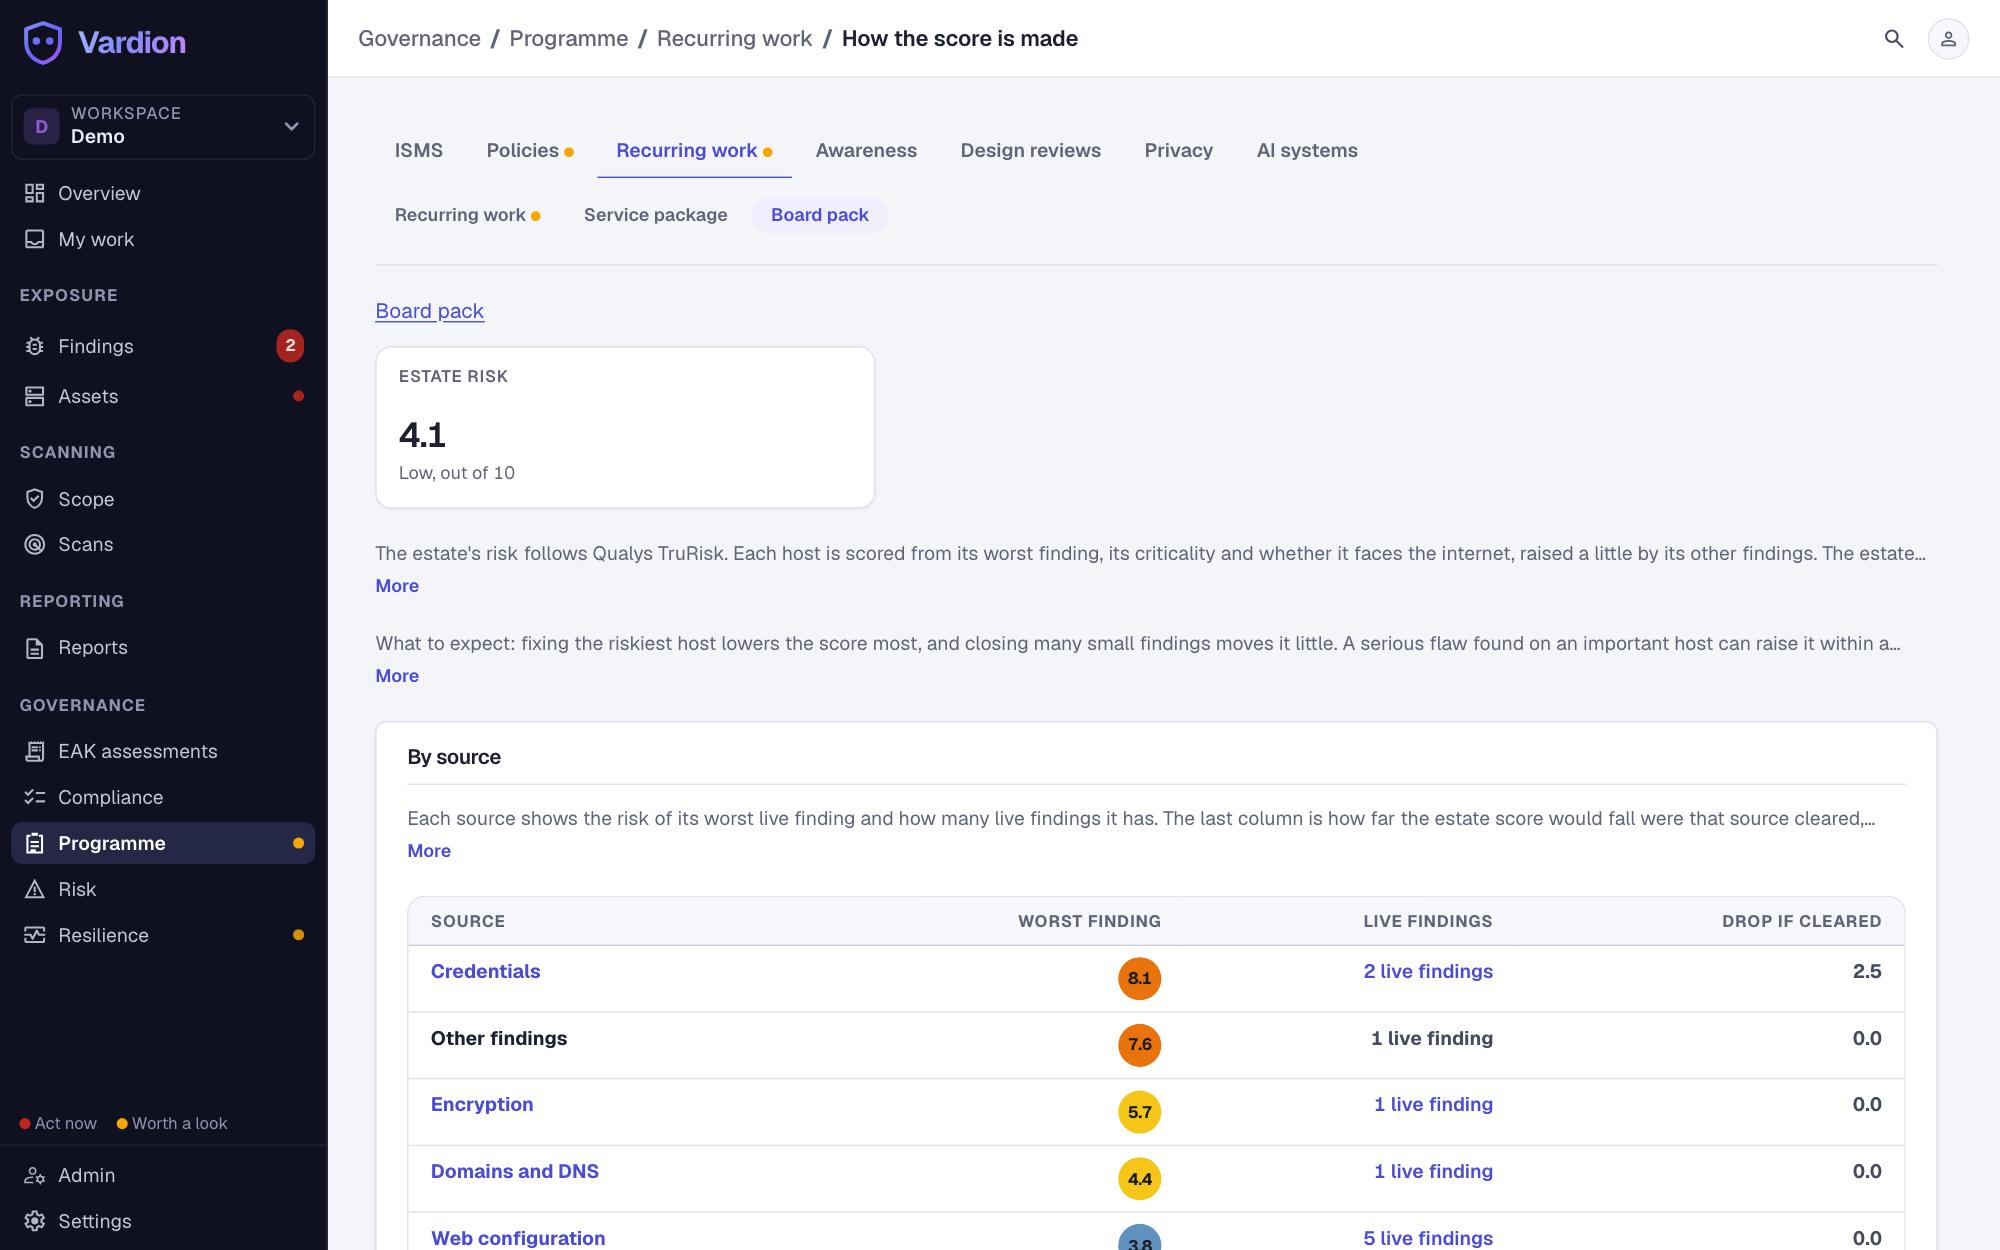
Click the score to see each host's part in it, then a finding, then its evidence and fix.
A summary your managing director will read
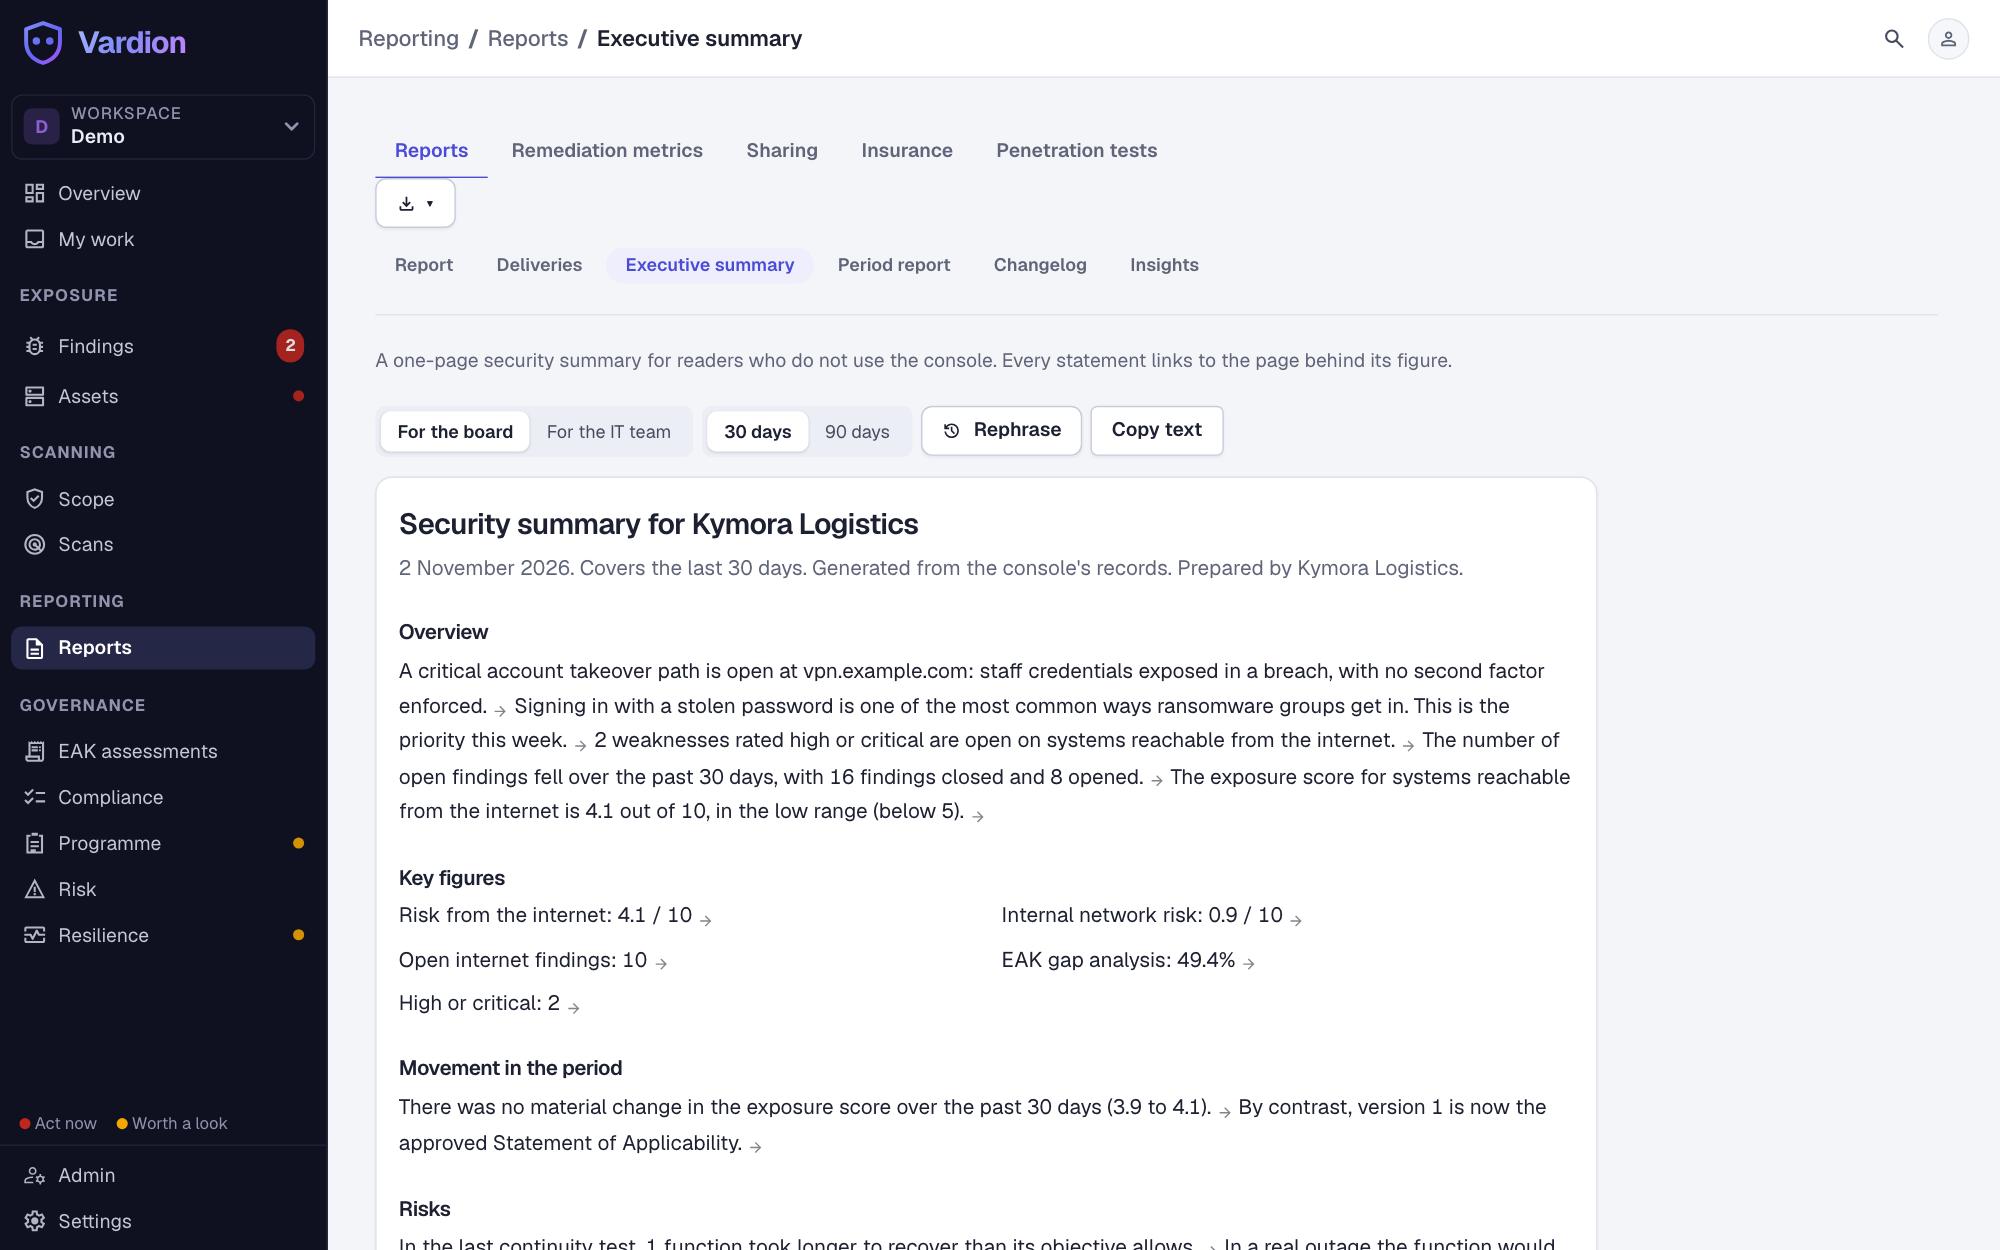
The score, the main risks, what changed and what the board must decide, on a page.
- A version for the board and one for the IT team, in English or Greek
- A full PDF report for anyone who will not open the console
Cyber risk in euros
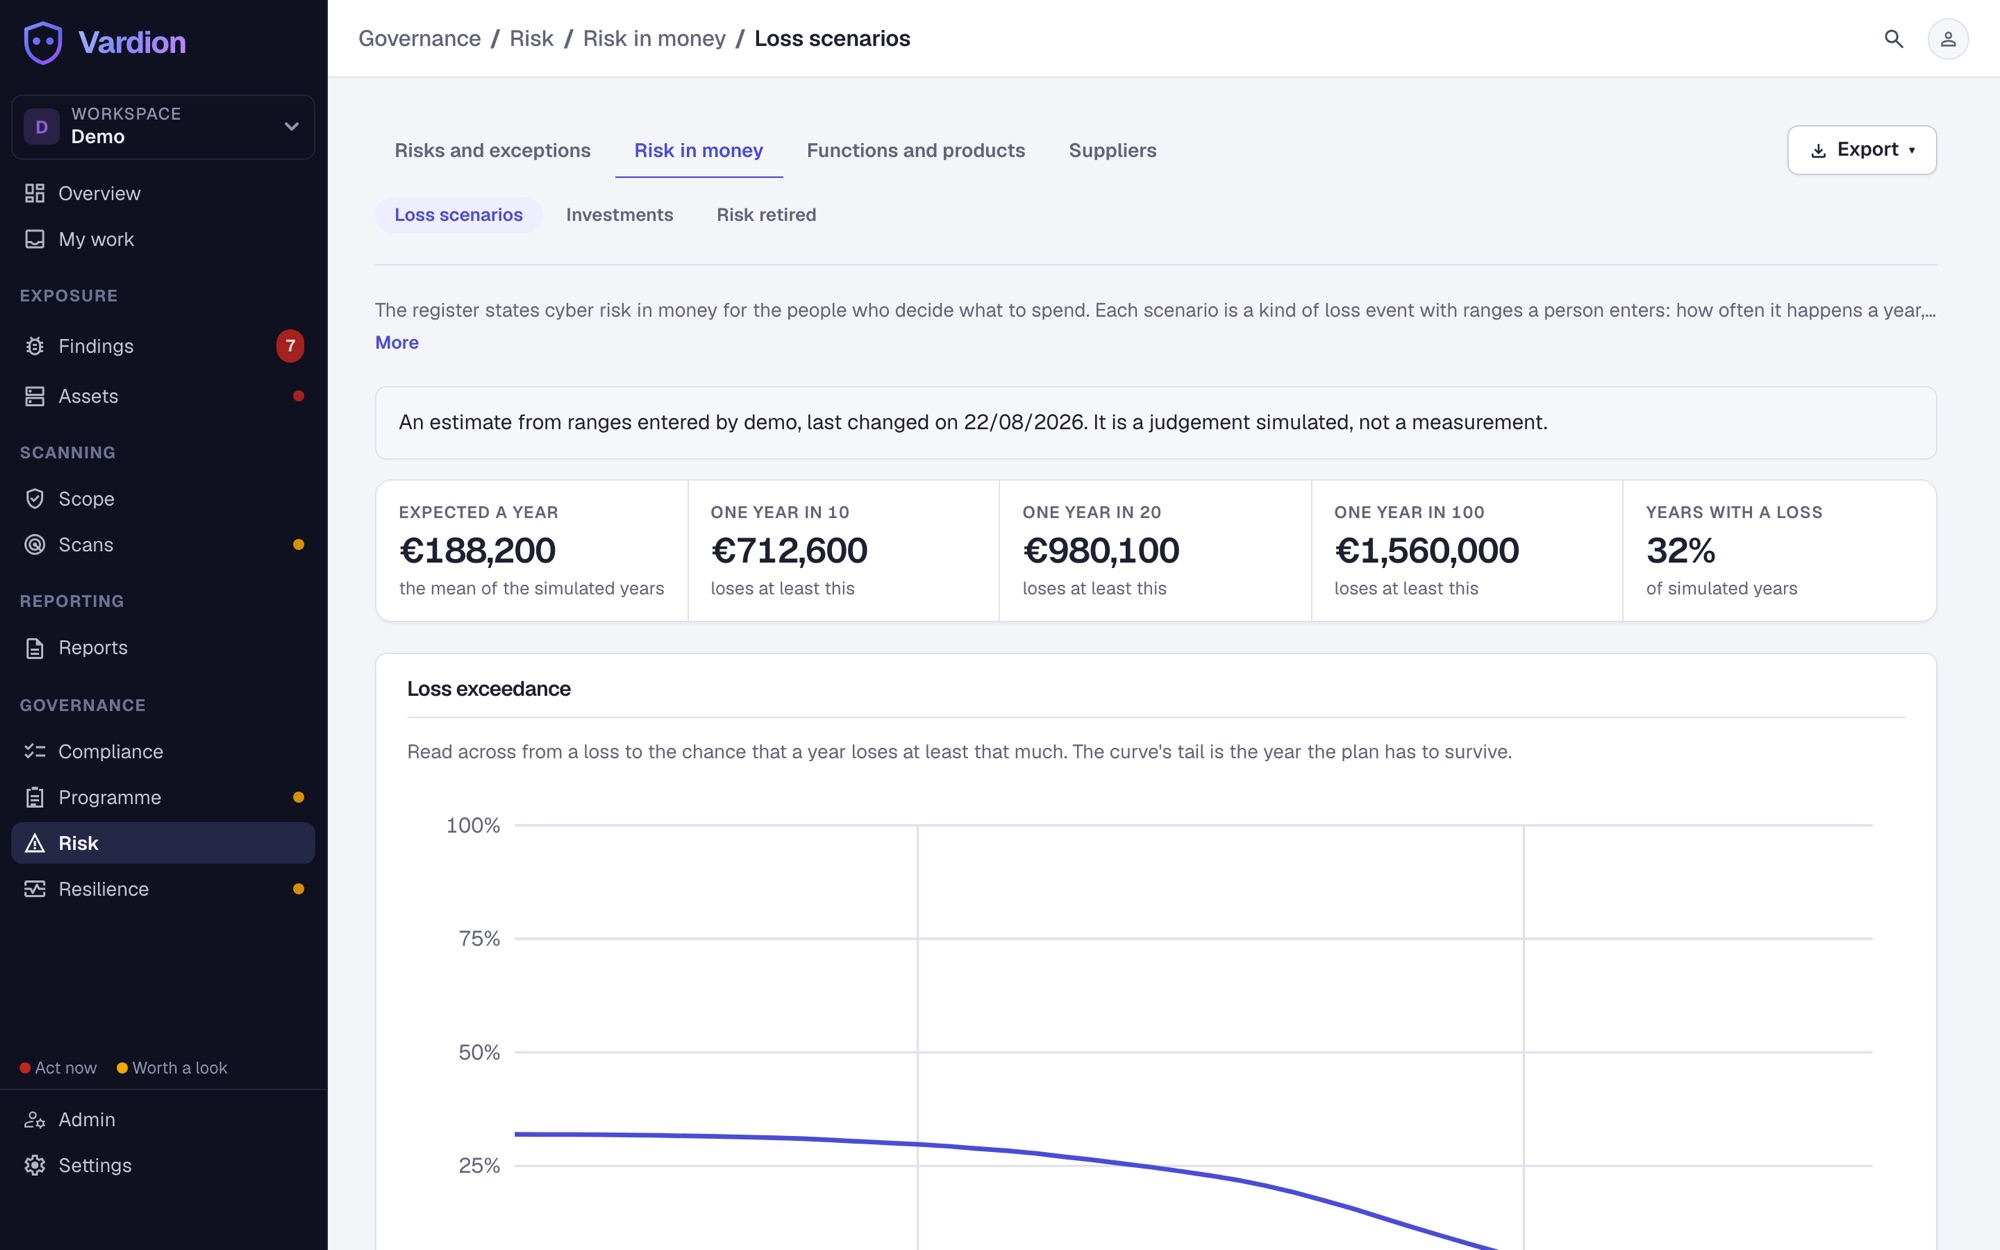
The expected loss a year and the one-in-100-year loss, by FAIR, the method that measures risk in money.
- See which control removes the most loss for each euro it costs
Security metrics
Days with no exploited flaw open
Counted from every full scan, on the overview and in the board pack.
Where risk gathers
The address, owner or product where risk concentrates.
How fast you fix
Median time to fix and the share fixed on time.
A monthly summary by email
The score, what opened and closed and the coming deadlines.
Frequently asked questions
Where do the euro figures come from?
From ranges your team enters for how often a loss happens and what it costs. The scans flag when a scenario's likelihood should rise.
Does it help with insurer and customer questionnaires?
Yes. It answers common security questions from insurers and customers from your scans, and shows what an insurer would see before your renewal.